Enterprise Cybersecurity & Network Defense Infrastructure
Patel Galaxify Solutions sizes, supplies, stages, and deploys high-throughput Next-Generation Firewalls (NGFW), Zero Trust network access gateways, IAM/PAM appliances, and security hardware. Engineered for resilient perimeter defense, deep SSL inspection, and Pan-India enterprise compliance.
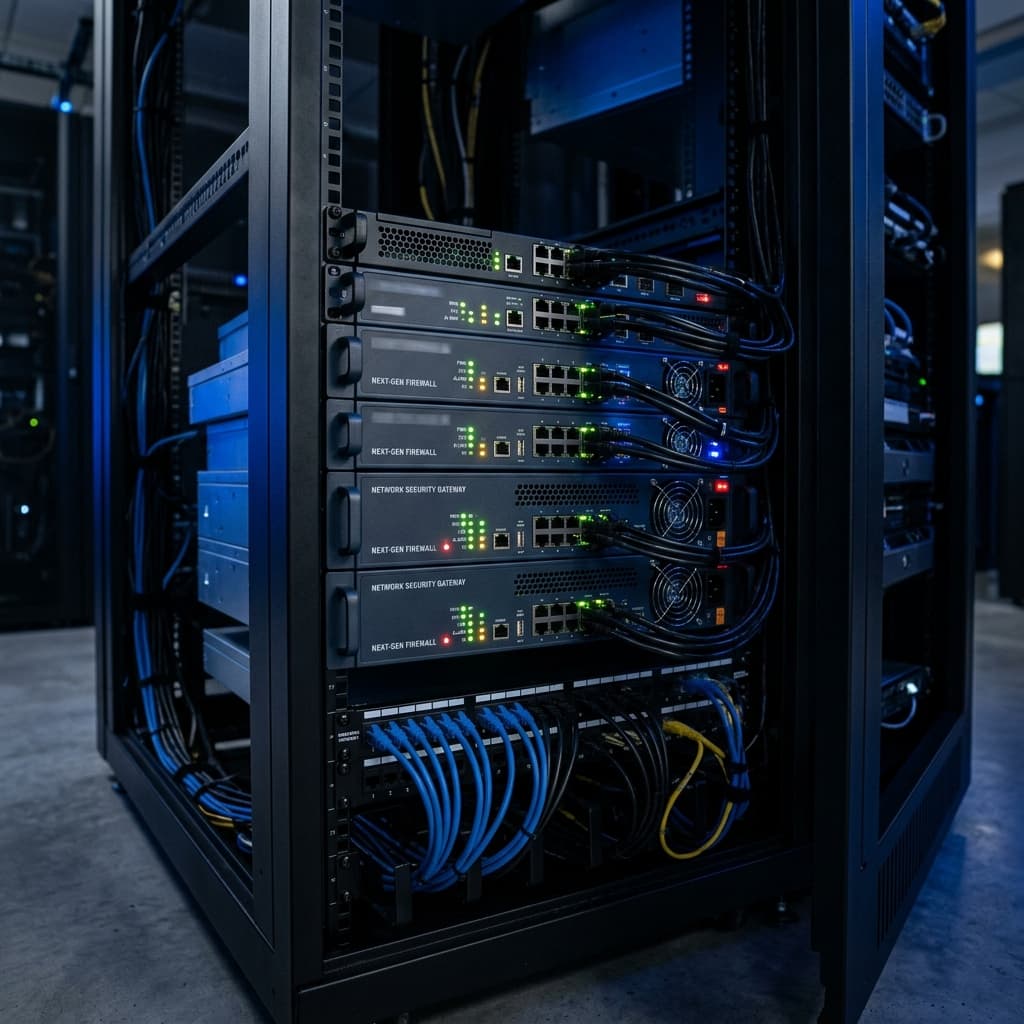
HIGH-THROUGHPUT NGFW CLUSTER
Dual active-passive firewall appliances with redundant uplinks
Enterprise Defense in an Asymmetric Threat Landscape
Legacy port-and-IP firewalls are inadequate against modern credential theft, automated lateral movement, and encrypted payload delivery.
Dissolving Enterprise Perimeters
Remote workforces, hybrid multicloud workloads, and distributed branch offices require dynamic Zero Trust micro-segmentation rather than static perimeter defenses.
Encrypted Attack Surfaces
Over 85% of enterprise web traffic is encrypted with TLS 1.3. Traditional security appliances suffer catastrophic throughput drops when executing deep SSL packet inspection without dedicated hardware ASICs.
Identity & Credential Vulnerabilities
Privileged account compromises remain the primary vector for ransomware propagation. Enforcing phishing-resistant MFA and hardware security tokens is vital to isolate infrastructure access.
Regulatory Compliance & Audit Rigor
Strict compliance standards (CERT-In directives, RBI cybersecurity frameworks, ISO 27001) demand immutable audit logging, network segmentation, and verifiable hardware provenance.
Enterprise Security Platforms Sized to Your Perimeter
Authorized hardware supply and implementation assistance covering premier enterprise security ecosystems including Fortinet, Palo Alto Networks, Cisco Systems, and Yubico.
Next-Generation Firewalls (NGFW)
Hardware-accelerated deep packet inspection, application-level visibility (App-ID), integrated intrusion prevention (IPS), and advanced threat protection engineered for corporate campuses and high-throughput data centers.
IDEAL DEPLOYMENT:
HQ perimeter gateways, data center edge inspection, high-bandwidth WAN aggregation, and encrypted SSL/TLS decryption.
KEY ARCHITECTURAL HIGHLIGHTS:
- Hardware-accelerated processing via dedicated security ASICs / NP processors
- Threat prevention throughput scaling from 1 Gbps to 40+ Gbps with full SSL inspection
- Dual hot-swappable AC power supplies with active electrical redundancy
- High-density 1G/10G SFP+ and 25G/40G QSFP+ interfaces for high-speed core uplinks
REPRESENTATIVE HARDWARE:
Fortinet FortiGate 100F/200F/600F Series, Palo Alto Networks PA-400/PA-1400/PA-3400 Series, Cisco Secure Firewall 3100 Series
Secure Access & SD-WAN Gateways
Converged networking and security gateways providing secure branch connectivity, dynamic path selection, application-aware routing, and Zero Trust Network Access (ZTNA) enforcement for distributed corporate footprints.
IDEAL DEPLOYMENT:
Regional branch offices, retail hubs, distributed manufacturing plants, and secure remote workforce aggregation.
KEY ARCHITECTURAL HIGHLIGHTS:
- Integrated SD-WAN with sub-second link failover across MPLS, Broadband, and 4G/5G links
- Zero Trust Network Access (ZTNA) client enforcement per-application rather than per-network
- Centralized cloud or on-premises management orchestrator with single-pane policy rollout
- Fanless desktop models for acoustic-sensitive branch environments or 1U rackmount for branch hub rooms
REPRESENTATIVE HARDWARE:
Fortinet FortiGate 60F/80F, Cisco Catalyst 8000 Edge / Meraki MX Series, Palo Alto Networks PA-400 Series
Identity, MFA & Hardware Security
Enterprise identity infrastructure, Privileged Access Management (PAM) server repositories, and FIDO2/WebAuthn hardware security keys providing phishing-resistant multi-factor authentication for administrators and staff.
IDEAL DEPLOYMENT:
Data center physical access, privileged sysadmin access, zero-trust workstation logon, and corporate single sign-on (SSO) enforcement.
KEY ARCHITECTURAL HIGHLIGHTS:
- FIDO2, WebAuthn, U2F, and smart card (PIV) standard compliance
- Crush-resistant, tamper-evident physical token construction with IP68 water resistance
- NFC and USB-A / USB-C dual interface support for workstations and mobile devices
- Compatible with major identity providers (Microsoft Entra ID, Okta, Ping Identity, Cisco Duo)
REPRESENTATIVE HARDWARE:
Yubico YubiKey 5 Series (5 NFC, 5C NFC, 5Ci), Dedicated Hardware Security Modules (HSMs)
Log Management & SIEM Infrastructure
High-IOPS on-premises server appliances sized specifically to ingest, index, and retain high-velocity syslog streams, firewall session logs, and telemetry data for CERT-In compliance and threat analytics.
IDEAL DEPLOYMENT:
Corporate security telemetry aggregation, compliance audit archives, on-prem SIEM hosts, and network packet capture repositories.
KEY ARCHITECTURAL HIGHLIGHTS:
- Dual Intel Xeon or AMD EPYC processors tuned for multi-threaded log parsing
- High-density NVMe write-cache tier paired with SAS storage pools for multi-terabyte log retention
- Redundant 10G/25G network interfaces dedicated to log ingestion and management planes
- Hardware RAID controllers with non-volatile flash-backed cache protecting telemetry in transit
REPRESENTATIVE HARDWARE:
Dell PowerEdge R760 Log Repositories, HPE ProLiant DL380 Gen11 Telemetry Nodes
Why Raw 'Firewall Throughput' Leads to Procurement Mismatch
Enterprise security appliances feature multiple published performance ratings that vary by orders of magnitude depending on enabled security inspection layers.
Raw Stateless Throughput
Evaluates only IP headers and TCP/UDP ports. Offers maximum theoretical bandwidth (e.g. 20–80 Gbps) but provides zero visibility into encrypted threats or application behaviors.
Threat Prevention Throughput
Engages IPS signatures, antivirus stream scanning, and App-ID. Demands intensive CPU cycles, typically yielding 25%–35% of raw firewall throughput.
SSL/TLS Deep Inspection
Full cryptographic handshake termination, packet decryption, threat scanning, and re-encryption. Patel Galaxify Solutions sizes your appliance specifically for this peak threshold.
Parameters Required for an Accurate Security BOM
To formulate a competitive, vendor-verified Bill of Materials with accurate license subscriptions, our security desk reviews these parameters.
Discovery & Traffic Profile Analysis
Security Sizing & Bill of Materials
Authorized Technology Sourcing
Physical Staging & Firmware Burn-In
Policy Deployment & Integration
Maintenance Contracts & Spares Logistics
Enterprise Cybersecurity Supply & Sizing FAQ
Guidance for Chief Information Security Officers, network architects, and procurement teams.
Does Patel Galaxify Solutions provide managed SOC services or penetration testing?
How do you size Next-Generation Firewalls for deep SSL/TLS inspection?
Are the firewall appliances and licenses genuine and registered with the OEM?
Do you support High Availability (HA) firewall pair configurations?
What ongoing hardware maintenance and replacement support is available?
Complementary Enterprise Solutions
Cybersecurity appliances deploy seamlessly alongside our enterprise compute, networking, and backup infrastructure.
Enterprise Networking Fabric
Spine-leaf data center switching, 10G/25G ToR switches, and enterprise core routing.
Enterprise Servers & Compute
Dual-socket rack servers, high-density compute nodes, and mission-critical virtualization hosts.
Backup & Disaster Recovery
Immutable backup repositories, ransomware-isolated storage targets, and disaster recovery appliances.
Specialized Technology Supply
Hardware security tokens, FIDO2 authenticators, industrial edge gateways, and enterprise collaboration tech.
Upgrade Your Enterprise Perimeter Defense
Connect with our security infrastructure specialists to review your peak encrypted throughput, select the right hardware form factor, and secure competitive RFQ pricing with pan-India delivery.